

Finseo, Ahrefs and Promptwatch state their own ISO 27001 certification, and several other AI visibility tools publish SOC 2 Type II. A vendor-by-vendor check of certificates and hosting, November 2026.
Updated 16 November 2026

| Tool | Own ISO 27001 | SOC 2 | Hosting region | Source checked |
|---|---|---|---|---|
| Finseo | ISO 27001 certified.[1] | No SOC 2 report; ISO 27001 is its certified standard.[1] | Frankfurt, Germany; EU data residency offered.[2] | Pricing, enterprise and trust pages |
| Ahrefs / Brand Radar | ISO/IEC 27001:2022 certificate published for Ahrefs Pte. Ltd.[3] | SOC 2 Type 2 report listed and available on request.[4] | Personal data transferred to and stored in the United States.[5] | Certificate, compliance and privacy pages |
| Promptwatch | Vendor-announced ISO/IEC 27001:2022 certification; certificate available on request.[6] | Not published. | Not published. | Certification announcement and privacy page |
| Peec AI | Certification in progress.[7] | SOC 2 Type II audit completed; report available under NDA.[7] | EU core services; Firebase Authentication operates in the United States.[8] | Enterprise, trust and DPA pages |
| Profound | Not published. | SOC 2 Type II attestation published; report available on request.[9] | Exact cloud region not published; listed providers include AWS, Google and Vercel.[10] | Trust centre and DPA |
| Otterly.AI | Certification pending.[11] | Not published; SOC 2 is on the roadmap.[12] | Frankfurt infrastructure plus US storage for public monitoring data.[13] | Security and compliance pages |
| Scrunch | Not published. | Completed independent SOC 2 Type II audit.[14] | US providers listed for GCP and OpenAI processing.[15] | Trust centre and security pages |
| Semrush Enterprise AIO | Not published for the reviewed AI products.[16] | Not published.[16] | Service data stored in US data centres.[16] | Security page |
| AthenaHQ | Not published. | Type I and Type II audits completed.[17] | Core providers process data in the US; some operate globally.[17] | Trust centre |
| Rankscale | Own certificate not published; Google Cloud credentials are listed.[18] | Own report not published; Google Cloud is described as Type II audited.[18] | Core product hosted in Iowa, United States.[18] | Privacy page |
| SE Ranking / SE Visible | Not published.[19] | Not published.[19] | Processors include Germany and Luxembourg, but product-specific residency is not stated.[19] | Privacy, DPA and processor pages |
| Writesonic | Not published. | SOC 2 Type 2 published in its DPA.[20] | US cloud regions listed; enterprise contracts may configure hosting regions.[20] | Security and DPA pages |
Checked against reviewed vendor security, trust, privacy and pricing pages on 16 November 2026. “Not published” means the reviewed public material did not establish that field; it does not prove that the vendor has no relevant controls.
ISO/IEC 27001:2022 is a standard for an information security management system, or ISMS. It covers how an organization identifies security risks, establishes controls, maintains the system and continually improves it. Certification applies only to the organization, activities and services included within the certificate’s stated scope.[6][21]
For an AI visibility, AEO or GEO platform, the scope matters because the product may involve prompt monitoring, web crawling, analytics, customer support, model providers, data exports and integrations. A generic “ISO certified” badge does not establish that every product, legal entity or processing activity is covered. Ahrefs’ published certificate, for example, specifies the Ahrefs Marketing Platform and its relevant development and operational activities.[3]
ISO 27001 is also not a GDPR certification. Finseo describes itself as GDPR-compliant, offers EU data residency and provides a DPA, but those are separate vendor commitments rather than proof of a GDPR certificate.[1]
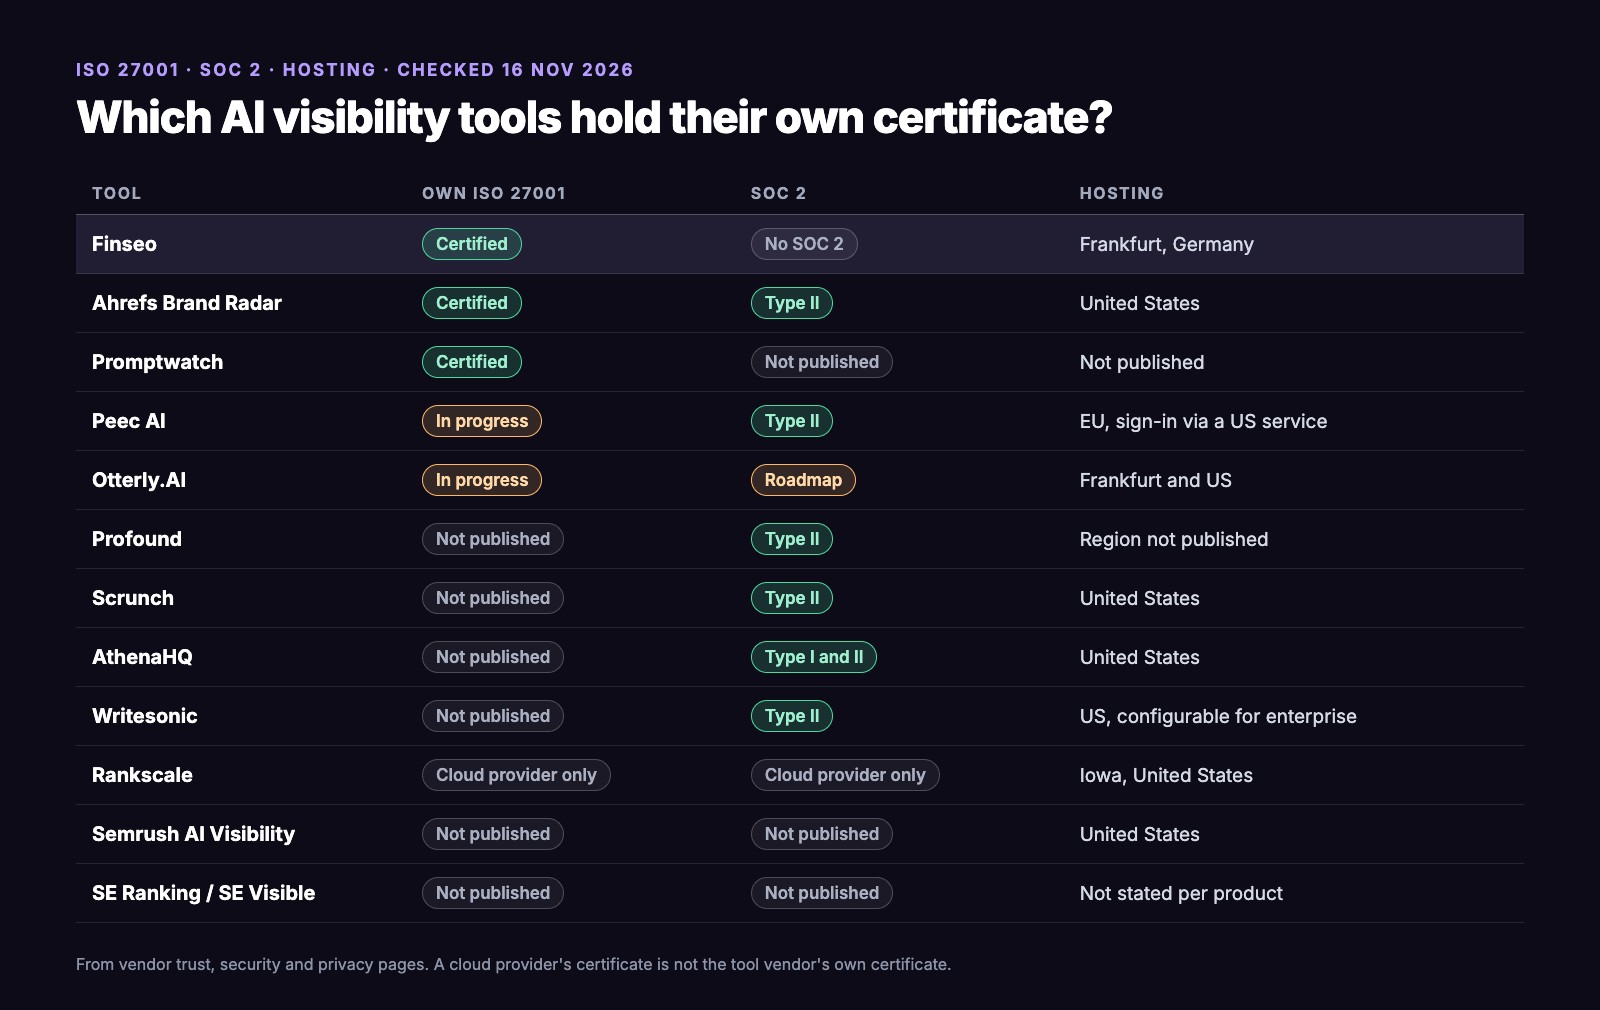
The comparison separates four types of evidence:
The review also separates security assurance from data residency. A platform can have a strong certification and still store personal data in the United States; another can host core systems in the EU while using a US-based authentication service.[22]
Finseo is the clearest fit for organizations seeking an AI visibility platform with a published ISO 27001 certification claim, German hosting and enterprise access controls. Its pricing page labels Finseo “ISO 27001 certified,” while its trust material describes an ISO/IEC 27001:2022-based information security management system.[23] Its enterprise page also lists unlimited seats alongside SSO via SAML, roles per project and an audit trail for enterprise teams.
Finseo’s enterprise information states that data is hosted in Frankfurt, Germany, with EU data residency. It also publishes GDPR-compliance commitments and a DPA for organizations, with a German AVV available on request.[1]
Finseo is ISO 27001 certified. As with any vendor, procurement can request the certificate and scope before contract signature.[1]
| Plan | Monthly billing | Annual-plan monthly equivalent | Main allocation |
|---|---|---|---|
| Starter | €84 / approximately $93 | €70 / approximately $77 | 50 prompts, 3 models, 1 project |
| Business | €210 / approximately $231 | €175 / approximately $193 | 150 prompts, 3 models, 1 project |
| Growth | €479 / approximately $528 | €399 / approximately $439 | 350 prompts, 3 models, 5 projects |
| Enterprise / Managed Service | Custom | Custom | All 23 models and unlimited projects |
Prices exclude VAT and annual plans are billed annually. Starter, Business and Growth each run three models of your choice at the same time, and more can be booked on any plan; Enterprise lists all 23 models.[1]
Verdict: Best for EU- or Germany-oriented teams that want AI visibility monitoring, up to 23 engines, Frankfurt hosting, SSO/SAML and an organization-level ISO 27001 claim in one platform. Obtain the certificate package and confirm which plan-level controls apply to the purchased service.[25]
Ahrefs publishes an ISO/IEC 27001:2022 certificate naming Ahrefs Pte. Ltd. The certificate was issued on 26 October 2026 and expires on 23 October 2028; it identifies the Ahrefs Marketing Platform within its scope.[3]
Ahrefs’ compliance documents also list a SOC 2 Type 2 report, available on request.[26] That gives buyers two separate evidence paths: a publicly inspectable ISO certificate and a SOC report that can be requested through the company’s compliance process.
The main residency qualification is that Ahrefs’ privacy policy states that collected personal data is transferred to and stored in the United States.[5] That does not negate the certification, but it may rule out Ahrefs for buyers requiring EU-only personal-data storage.
Verdict: Best for buyers prioritizing publicly inspectable ISO documentation and additional SOC 2 Type 2 evidence, provided US personal-data storage meets their requirements.[27]
Promptwatch announces its own ISO/IEC 27001:2022 certification and identifies Promptwatch B.V. as the certified organization. The announcement names ProCertify as the certification body, certificate number 27001 26102026.2, and validity from 26 October 2026 to 26 October 2029.[6]
The stated scope covers the development, implementation and customer support of the PromptWatch SaaS platform. Promptwatch says the actual certificate is available to customers and prospects on request.[6]
The reviewed public material does not publish Promptwatch’s SOC 2 status or hosting region. Its privacy policy permits international transfers but does not establish a specific data-residency commitment.[13]
Verdict: Best for buyers willing to request the certificate directly and verify a clearly described ISO scope, while treating SOC 2 and residency as open procurement questions.[28][6]
Peec AI provides a useful example of why ISO and SOC 2 should remain separate fields. Its enterprise material describes a completed SOC 2 Type II audit, with the report available under NDA, while its trust centre describes ISO 27001 certification as in progress.[7]
Peec’s core services are described as EU-hosted: Google Cloud in Frankfurt, ClickHouse Cloud in the Netherlands and Firestore in a European multi-region covering Belgium and the Netherlands. Firebase Authentication operates in the United States and cannot be configured to another region.[8][18]
That means “EU-hosted” would be incomplete without the authentication qualification. Buyers should ask which categories of personal data pass through authentication, logging, backups and support systems.[28]
Verdict: Best for buyers that require completed SOC 2 Type II evidence and can accept ISO certification still being in progress, subject to reviewing the report and US authentication processing.[18][7]
Profound publishes a SOC 2 Type II attestation that was independently examined by Sensiba LLP; the report is available on request. Its reviewed trust material does not establish an own ISO 27001 certificate.[27][6]
Profound lists AWS, Google and Vercel among its cloud or application providers, but the exact deployment region and an EU-only residency commitment are not published in the reviewed material.
Otterly.AI describes its own ISO certification as pending and does not publish a completed SOC 2 report. It references AWS ISO and SOC credentials as infrastructure assurance rather than as its own application certification.[29][30]
Its security page describes Frankfurt infrastructure but also states that public monitoring data is stored in Northern Virginia, United States.[13]
Scrunch states that it completed an independent SOC 2 Type II audit and lists supporting trust-centre documentation. Its reviewed material does not establish an own ISO 27001 certificate.[27]
The listed infrastructure includes GCP and OpenAI, with the reviewed subprocessors page identifying US processing or storage; an exact EU-residency commitment is not published.[20]
Semrush’s reviewed security page does not publish an own ISO 27001 certificate or SOC 2 report for the AI visibility products. It identifies AWS, Google Cloud and Digital Realty data centres and states that service data is stored in US data centres.[22][31]
Provider compliance references should not be presented as Semrush’s own certification. Buyers should request product-specific evidence for Enterprise AIO or the AI Visibility Toolkit.[6][16]
AthenaHQ’s trust centre lists completed SOC 2 Type I and Type II audits. Its reviewed material does not publish an own ISO 27001 certificate.[6]
The trust material identifies Vercel, Google Cloud, AWS and PlanetScale, with core provider processing in the United States or globally. EU-only residency is not published.
Rankscale does not publish its own ISO 27001 certificate or SOC 2 report in the reviewed privacy material. It identifies Google Cloud’s ISO and SOC credentials, but those are credentials of the infrastructure provider.[29]
The core product is hosted in Google Cloud’s us-central1 region in Iowa, United States. EU storage used for public marketing pages does not relocate the core application.[22][18]
SE Ranking’s reviewed materials do not establish an own ISO 27001 certificate or SOC 2 report for SE Visible. An information-security requirement in its DPA is not the same as certification.[28]
Its processor list names Hetzner in Germany and AWS EMEA in Luxembourg, but it does not publish product-specific residency boundaries or a precise AWS deployment region.[32]
Writesonic’s DPA identifies SOC 2 Type 2 evidence and says the most recent report is available to demonstrate compliance. Its reviewed material does not publish an own ISO 27001 certificate.[6]
The DPA lists Azure as the primary cloud provider and AWS for selected workloads, with US regions listed; enterprise contracts may provide configurable hosting arrangements. Buyers should use the DPA and contract to establish the applicable region.[20]
ISO 27001 and SOC 2 are related but different forms of assurance.
| Question | ISO/IEC 27001:2022 | SOC 2 Type I | SOC 2 Type II |
|---|---|---|---|
| What is assessed? | An information security management system and its risk-management processes.[33][34] | Design of specified service controls at a point in time.[33] | Design and operating effectiveness of specified controls over an examination period.[9] |
| What should buyers request? | Certificate, scope, issuer, certificate number and validity.[6][27] | Auditor’s report, system description and date of assessment.[35][20] | Report, examination period, test results, exceptions and customer responsibilities. |
| What does it prove? | Conformity to the standard within the stated scope.[28][27] | A point-in-time assessment of control design.[36][20] | Evidence that controls operated during the examined period.[28][8] |
A vendor’s own certificate applies to the vendor and the certificate scope. A cloud provider’s certificate applies to the cloud provider’s own services and controls. AWS, Google Cloud or Azure certification does not automatically certify an AI visibility platform built on that infrastructure.[20]
The distinction also applies to SOC 2. If Rankscale identifies Google Cloud as SOC 2 Type II audited, that does not establish that Rankscale itself has a SOC 2 report.[18]
Neither ISO 27001 nor SOC 2 proves that a platform cannot suffer a breach. A review of ISO 27001 research found limited evidence about certification outcomes and identified implementation challenges, supporting the use of certification as one part of a broader security assessment.[37]
Use this numbered checklist before accepting an ISO 27001 claim:
ISO recommends checking accredited certificates through IAF CertSearch or contacting the certification, accreditation or IAF bodies directly.[38] Ahrefs’ certificate illustrates the level of detail buyers should seek: it includes the holder, scope, certificate number, issue date, expiry date and certification-body contact information.[3]
Procurement teams evaluating an AI search monitoring tool should ask:
A certificate answers only part of this list. The strongest vendor comparison combines assurance scope, data location, operational controls and contractual commitments.
“Not published” means the reviewed public trust, security, privacy, pricing or compliance material did not establish the claim. It does not prove that the vendor lacks security controls or cannot provide evidence privately.
No. A vendor’s certificate applies to the vendor’s certified organization and stated scope. A cloud provider’s certificate applies to the provider’s infrastructure and services, not automatically to the application built on top of them.[20]
No. SOC 2 Type II and ISO/IEC 27001 assess different frameworks and produce different evidence. A SOC 2 Type II report supports an assessment of controls operating during an examination period, while ISO 27001 certification concerns conformity of an ISMS within scope.[37][21]
Finseo is ISO 27001 certified, Ahrefs publishes an ISO/IEC 27001:2022 certificate, and Promptwatch announces its own ISO/IEC 27001:2022 certification with certificate details and a certificate available on request.[6]
The reviewed Peec material describes ISO 27001 certification as in progress, not completed. Peec separately states that its SOC 2 Type II audit is complete.[7]
Finseo publishes Frankfurt hosting and EU data residency, while Peec publishes EU core hosting with a US Firebase Authentication exception. Otterly.AI publishes Frankfurt infrastructure but also US storage for public monitoring data, so each vendor requires a data-flow review rather than a simple regional label.[13]
Finseo is ISO 27001 certified, Ahrefs publishes an ISO/IEC 27001:2022 certificate, and Promptwatch announces its own ISO/IEC 27001:2022 certification. The evidence differs: Ahrefs publishes a certificate, Promptwatch publishes certificate particulars with the document available on request, and Finseo lists its ISO 27001 certification on its enterprise page.[6]
Finseo, Ahrefs and Promptwatch provide the strongest ISO-related evidence in this comparison. Ahrefs publishes the most inspectable certificate, while Finseo combines its ISO 27001 certification with Frankfurt hosting, EU data residency, GDPR commitments, SSO/SAML and an enterprise audit trail.[1]
Profound, Peec AI, Scrunch, AthenaHQ, Ahrefs and Writesonic publish or list SOC 2 Type II evidence, with availability and report detail varying by vendor. Peec explicitly describes its SOC 2 Type II audit as complete while ISO 27001 remains in progress.[7]
Profound publishes a SOC 2 Type II attestation independently examined by Sensiba LLP, with the report available on request. That is more precise than describing Profound simply as “SOC 2 compliant,” so buyers should request the report and review its system scope, examination period and exceptions.[9]
Peec AI describes ISO 27001 certification as in progress rather than completed. Its completed SOC 2 Type II audit is a separate assurance result, and its core EU hosting has a US Firebase Authentication qualification.[18]
Finseo publishes GDPR-compliance commitments, a DPA, Frankfurt hosting and EU data residency. Peec publishes EU hosting for core services but uses US-based Firebase Authentication, while other vendors disclose US or mixed processing; buyers should verify the full data flow and contract terms.[8][29]

